Open to Full-Stack & Forward-Deployed AI Engineer Roles
Hamza Ali·Full-Stack AI & LLM Systems Engineer — Multi-Agent Workflows, Enterprise RAG & MCP
Production AI systems that prove their answers.
I build the whole stack so production AI staysaccess-controlled.
Full-stack AI engineer building the whole vertical slice: FastAPI backends, React frontends, hybrid retrieval pipelines, MCP tool servers, eval harnesses, and Docker Compose deployments — ready to partner directly with product and client teams to ship AI into real workflows.
NOAA lightning telemetry & Tableau risk map at ATS AI Lab
[01//flagship work]
Three end-to-end AI platforms, built for real failure modes.
Packaged with Docker Compose and documented with Architecture Decision Records, evaluation harnesses, and narrated walkthroughs — inspect the full code and trade-offs behind each system.
Inspect the architecture, protocols, evals & token economics.
Step through authorization boundaries and fallback states, inspect all 8 MCP JSON-RPC tool schemas, review scoped repository benchmarks, and model LLM caching costs.
Owning the whole stack from retrieval to deployment.
The Engineer Behind the Systems
Hamza Ali
Full-Stack AI
Full-stack engineer focused on AI systems that hold up outside a notebook. I build the entire vertical slice — FastAPI backends, React frontends, hybrid retrieval pipelines, evaluation harnesses, and Docker Compose deployments — so nothing gets lost in handoff between prototype and production.
Most AI demos skip the unglamorous engineering that actually decides whether a team can trust the system: per-request access control before the LLM ever runs, deterministic static scanners that constrain what agents can claim, durable webhook job queues, and automated regression tests (90 in FinSight, 690+ in AI Code Review Agent) that measure when the model is wrong.
Before focusing full-time on LLM systems, I bridged academic CS foundations and operational analytics at ATS AI Lab — turning ~1 million NOAA lightning-strike records into Tableau risk-zone recommendations — and regularly mentored fellow engineers on architecture and technical decisions. I'm looking for a full-stack or forward-deployed AI engineering role working directly with product and client teams to get AI into real workflows.
Engineering Standard
Every system ships with clear access boundaries, reproducible Docker Compose packaging, automated regression tests (90 & 690+), and honest measurement of where models fail.
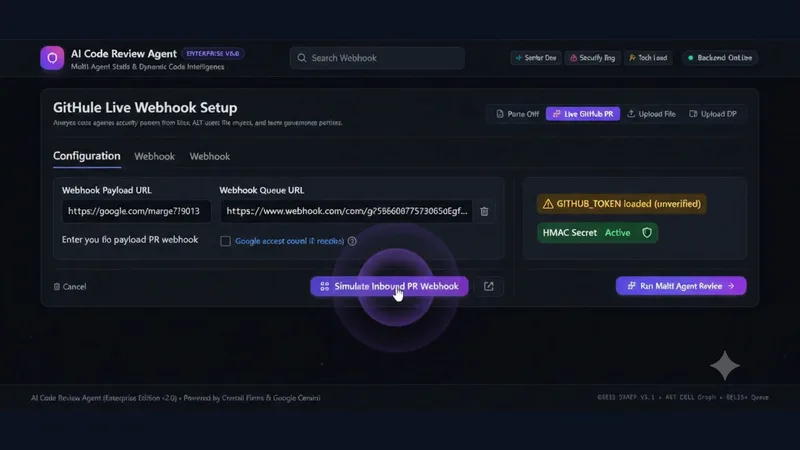
Built AI Code Review Agent — deterministic-first multi-agent PR review platform (3-agent CrewAI Flows crew + plain-code reconciler), durable SQLite WAL webhook queue, 15 PR slash commands, 8-tool MCP server, SARIF v2.1.0, and 690+ tests across Python 3.10–3.13.
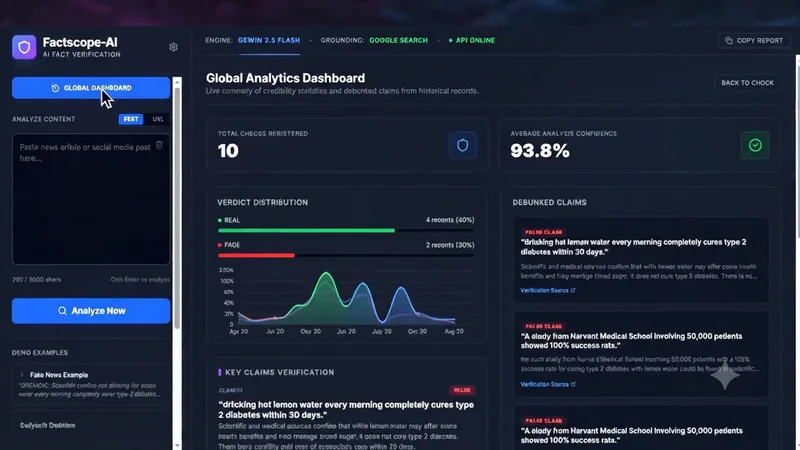
Delivered Factscope AI — full-stack claim decomposition & Google Search-grounded verification platform with 3-tier quota failover across Web and Electron 36 desktop.
Supervised & unsupervised learning, bias/variance & model evaluation
[04//engineering notes]
How I think about failure modes & trade-offs.
Short architectural notes written directly from production trade-offs encountered while building FinSight, AI Code Review Agent, and Factscope AI.
Note 01FinSight3 min note
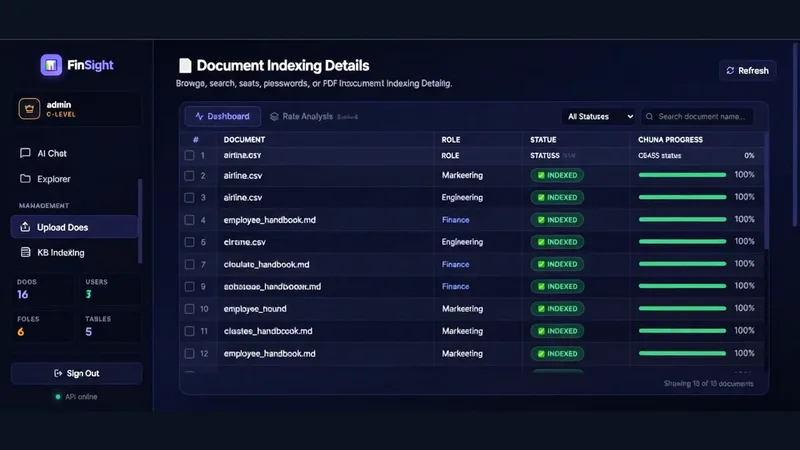
Why Authorization Must Happen Before Retrieval & LLM Routing
Prompt instructions are not an access-control boundary. In enterprise RAG, permissions must be enforced before any embedding search, SQL query, or model call.
Many RAG prototypes retrieve top-k chunks first and tell the LLM in the system prompt to 'ignore documents the user should not see.' That pattern fails immediately under prompt injection and still leaks sensitive tokens into model context.
In FinSight, department access runs across three independent layers: JWT verification with per-request DB role re-validation, a zero-token pre-LLM department guard, and hard ChromaDB metadata filters plus an isolated in-memory DuckDB table whitelist (`enable_external_access=False`).
The automated RBAC security suite scored 0.93 with zero metadata-filter violations, while transparently surfacing a general-doc 'revenue' phrase calibration note — proving why access boundaries must be measured with regression tests, not assumed.
Key Engineering Takeaways
Re-validate the user's current database role on every JWT request so revoked roles cannot query stale permissions.
Block cross-department intent in a pre-LLM guard to eliminate both data leakage and wasted token spend.
Isolate Redis cache keys by role digest (`finsight:query:{role}:{digest}`) so repeat queries replay in < 20ms without cross-tenant bleeding.
Run Deterministic Checks First to Limit What Agents Can Claim
Sending raw diffs straight to an LLM invites hallucinated reviews. Running static scanners, AST call graphs, and a plain-code reconciler constrains agent output to verifiable facts.
Note 03Factscope AI3 min note
Designing LLM Backends That Degrade Honestly Under Quota Pressure
LLM APIs and search grounding tools have separate rate limits. Production apps need multi-tier failover, error classification, and transparent UI state when grounding is unavailable.
Every framework, database, and security layer listed below maps to real code in FinSight, AI Code Review Agent, Factscope AI, or ATS AI Lab — zero resume filler.
Google Gemini & GenAI SDK
Grounded Generation, Routing & Failover
Gemini 2.5 Flash & 3.1 Flash Lite with Google Search grounding, structured outputs, fallback chains, and gemini-embedding-2-preview.
Processed ~1M NOAA lightning-strike telemetry records into Tableau risk heatmaps and operational recommendations at ATS AI Lab.
[06//collaboration]
Open for full-stack & forward-deployed AI roles & selective advisory.
Looking for a full-stack or forward-deployed AI engineering role where I work directly with product and client teams to get AI into real workflows — plus selective architecture & evaluation engagements.
Hiring a Full-Stack or Forward-Deployed AI Engineer?
I own the full vertical slice — FastAPI backends, React/TypeScript UIs, hybrid RAG + 3-layer RBAC, CrewAI/MCP agent workflows, 780+ automated tests, and Docker Compose deployments — working directly with engineering and client teams remotely (UTC+5).
Production knowledge workspaces enforcing department permissions before retrieval, blending dense + BM25 hybrid search, and isolating structured SQL analytics.
3-layer RBAC: JWT role re-validation, pre-LLM guard & store filters
Measure when models are wrong and harden brittle prototypes with RAGAS/DeepEval harnesses, quota-free regression suites, failover chains, and cost/latency tuning.
Full-Stack AI & LLM Systems Engineer · Python, FastAPI, React & LLM Systems
Open to full-time remote Full-Stack AI and Forward-Deployed AI Engineer roles working directly with product or client teams, as well as selective consulting on RAG, multi-agent pipelines, and evaluation harnesses.
Open to Full-Stack & Forward-Deployed AI Engineer Roles